AI Adopts: AI Governance Challenges for Small Teams 2026
⏱️ 4 Mins Read
As AI adopts more everyday work tasks, the biggest AI governance challenge for small teams 2026 is visibility, not regulation. Surveys published in 2026 put unauthorized AI use at 55% to 64% of employees, while estimates for formal ISO 42001 certification are negligible. A free US framework offers a cheaper starting point. No study separates companies with under 50 employees from those with more, so the figures below reflect larger or mixed samples.
📌 Executive Brief
- Shadow AI is common: 55% of US employees (Upwork) and 64% at 50-to-500-person firms (WatchGuard) admit using unapproved AI tools.
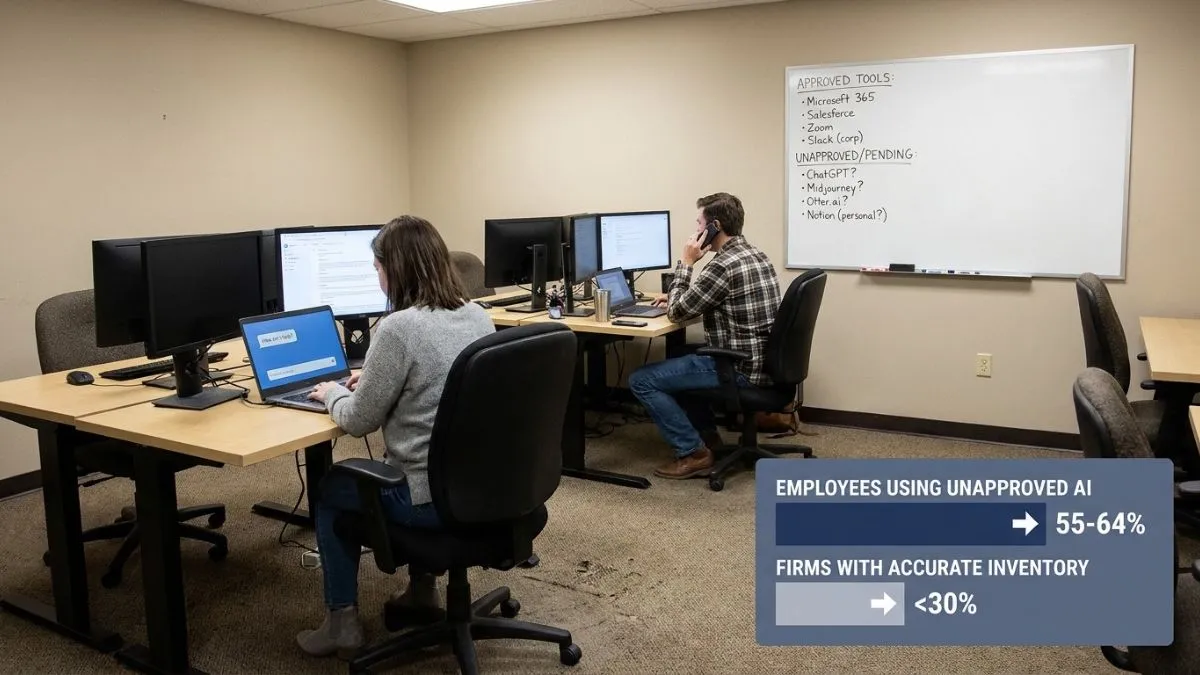
- Visibility is thin: fewer than 30% of surveyed employees at mid-sized firms believe their company keeps an accurate software inventory.
- Costs vary widely: consultancy estimates for ISO 42001 certification range from about £8,000 to £110,000, depending on size and scope.
- Rules are moving: South Korea’s AI Basic Act took effect in January 2026, and the EU’s Digital Omnibus entered into AI Regulation on July 27, 2026.
Shadow AI: The Main Exposure
The Upwork Research Institute’s 2026 Future Workforce Index, a survey of 2,400 US workers in March and April, found that 55% of full-time employees admit to using unapproved AI tools at work.
WatchGuard’s July 2026 survey of 684 employees at companies with 50 to 500 staff, across eight countries including the US and Mexico, put the figure at 64%. The same survey found that fewer than 30% of respondents believe their organization keeps an accurate inventory of the software in use, and nearly 40% said the company lacks full visibility into the applications employees run. WatchGuard noted the data is self-reported.
Large companies are not immune. PagerDuty’s 2026 survey of 1,250 office professionals at companies with at least $500 million in revenue found 66% had used AI tools they believed were not permitted.
This is why AI data transformation work, such as cleaning, summarizing, or reformatting customer records, is where small teams are most exposed: the task is routine, and the data often goes through a personal chatbot account.
Supplying an approved tool does not end the habit. Deel, citing Gartner’s Q1 2026 survey of 12,004 employees and managers in 40 countries, reports that 88% of employees with an employer-provided AI tool also use a personal one for work.
Managers also tend to overestimate what they can see. Okta’s survey, reported by The Register in May, found 90% of executives were confident in their organization’s visibility into AI tools, even though more than half of knowledge workers admitted to using AI tools without approval. More than half of the organizations surveyed also reported an AI-related security incident or near miss in the past year.
What are the latest AI trends in 2026?
The defining trend for small teams in 2026 is employee AI use outrunning company policy: surveys put unapproved use at 55% to 64%. South Korea’s AI Basic Act took effect in January, while in the EU, the Digital Omnibus entered into force with AI Regulation (EU) 2026/1744 on July 27, 2026. The EU’s Digital Omnibus, in force since 27 July, delays high-risk rules to December 2027 but left transparency duties on schedule.
Will AI replace compliance?
No. Automated tools can speed up parts of compliance, such as discovering which AI tools staff use, but laws and frameworks assign accountability to organizations and people. Surveys also show a visibility gap: Okta found 90% of executives were confident about AI visibility while more than half of workers admitted unapproved use.
Which country has an AI governance framework in 2026?
South Korea’s AI Act took effect on 22 January 2026 and covers impact, safety, and transparency for generative AI. Fines are expected to begin in January 2027, after a one-year grace period. The EU’s AI Act is now phasing in.
According to law firm Cooley’s analysis, the Korean law applies to foreign AI systems that affect users or markets in the country. Fines are capped at 30 million won.
In the EU, the Digital Omnibus on AI, Regulation (EU) 2026/1744, entered into force on 27 July 2026. It moves standalone high-risk obligations from August 2, 2026, to December 2, 2027, and embedded high-risk AI from August 2, 2028, to August 2, 2028. Orrick says it also extends SME simplifications to “small mid-cap” companies. The delay moves the date, not the obligation.
What is the 30% rule of AI?
It is not a legal or standards-body rule. Online, it usually means one of three things: AI handles 70% of work and people 30%; the reverse, automating 30% first; or a 30% AI-detection threshold in academic checks.
The interpretations conflict, and tech outlets such as BGR note that the rule’s origins are hard to trace. For governance purposes, treat it as a rough heuristic about human oversight, not a compliance benchmark.
Compliance Costs For Small Teams?
Public cost data is thin, and nearly all of it comes from consultancies and tooling vendors that sell certification support. ISO/IEC 42001, the AI management system standard, was published in December 2023, and one vendor’s own calculator describes its benchmarks as “directional” rather than survey-grade.
| ISMS.online (UK consultancy) | 1 to 50 staff | £8,000 to £110,000 |
| CertPro (consultancy) | Small to mid-sized, initial certification | $15,000 to $60,000 |
| Hicomply (compliance software) | Small AI vendors, first year | £25,000 to £60,000 |
| Elevate (consultancy) | 50 to 200 employees | $85,000 to $150,000 |
Audit fees are only part of the bill. CertPro puts certification-body fees at $5,000 to $25,000 for the initial audit, with annual surveillance audits at $3,000 to $12,000. Elevate says implementation work typically costs two to three times the audit fee.
The spread is the finding. The same-size company can be quoted a few thousand pounds or well over $100,000, and scope matters more than the vendor. Compliance costs at this scale can work as a moat if customers or regulators start demanding it. Certification is also optional. The US NIST AI Risk Management Framework is free and voluntary, though NIST says its companion Playbook is neither a checklist nor a set of steps to follow in full.
Responsible AI governance framework design patterns for a small team
The NIST framework (AI RMF 1.0, published January 2023) is built around four functions: Govern, Map, Measure, and Manage. Govern sets policy and accountability, while the other three are applied to each AI system. A small team can adopt a responsible AI governance framework by starting with the first two, as the following design patterns show. These are editorial suggestions, not requirements of the framework:
- Name one owner. Accountability is the governance function, and in a small firm it can sit with one person.
- Write a one-page acceptable-use policy. State which tools are approved and which data must never be entered.
- Keep a live inventory: map which AI tools are used and what data they touch. The WatchGuard figures suggest most firms do not know.
- Offer an approved option, then check. The Gartner figure above shows that approval alone is not enough, so review actual usage periodically.
AI value, risks, mitigation strategies, and benefits
The value is speed on routine work. The risks are unapproved tools, data leaving the company, and a lack of inventory. The cheapest mitigation strategies are policy, ownership, and a tool list; the benefit is answering a customer’s AI questions without a certification project.
Limits of the data
No survey cited here isolates companies with fewer than 50 employees. Every shadow-AI figure is self-reported, and several come from vendors with products to sell. The cost estimates come from consultancies and cannot be compared like-for-like, since currencies, scopes, and company sizes differ. We found no head-to-head study comparing lightweight governance with enterprise compliance suites.
For AI governance challenges for small teams in 2026, the evidence points to a visibility problem more than a spending problem. A named owner, a one-page policy, and an AI-tool inventory address the most common exposure at close to zero cost. Formal certification is a separate decision, driven by customers and regulators rather than by the technology.
Read more analysis in our Global Business section.